 VANCORD
Incident Readiness Short Assessment
12-Question Cybersecurity Self-Assessment
How Ready Is Your IT Team for a Security Incident?
Small IT teams have to keep systems running, support users, and manage an ongoing stream of security threats. This 12-question self-assessment draws on selected areas of the NIST Cybersecurity Framework (CSF) 2.0 to give you a short overview of where your security coverage appears strong and where ownership, detection, response, or recovery may need a closer look.
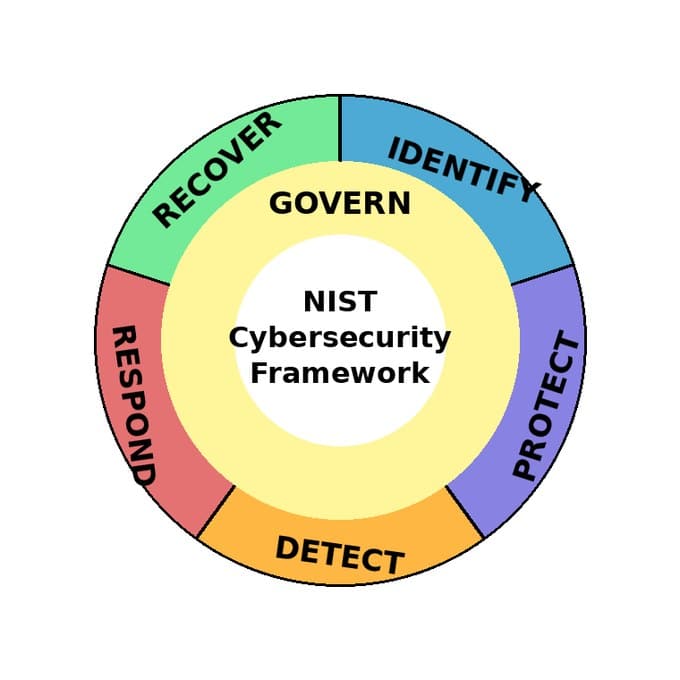
A short overview, not a detailed assessment.
This self-assessment touches selected areas of the NIST CSF 2.0 to help surface issues worth a closer look. It is not a full NIST assessment or audit.
Use your score as a starting point for deciding where a deeper review may be useful.


What you get
See your basic readiness score right away, with no email required. If you want a closer look afterward, you can set up a free-of-charge consultation with a Vancord security engineer to review the results and walk through the full Vancord assessment. You can also request a customized PDF summary after completing the self-assessment.
| Question | Yes | Partial | No | Don't know | N/A |
|---|
Readiness Intelligence Brief
Use this as a conversation starter: it shows where readiness appears strongest, where it may fail first, and what to validate before this becomes an executive, insurance, legal, or operational problem.
This readiness score is a screening result, not an audit finding. It summarizes the current answers and should be validated against evidence.
Executive snapshot
—
What this score suggests
—
Where readiness may fail first
—
How to start the internal conversation
—
Conversation starter
—
First validation action
—
Defense wall snapshot
The wall is a prioritization heuristic. In incident readiness, the weakest operational function often determines where the response will break first. Use it to decide what to validate first, not as a mathematical proof of total risk.
—
Category dashboard
These six functions follow the NIST Cybersecurity Framework structure. Use this dashboard to read each score as a diagnostic signal and as a prompt for the first validation conversation.
Three areas to look at first
Your answer log
This table shows every answer used to produce the score. It is intentionally kept in the on-page report so a reviewer can see the evidence trail before downloading or customizing anything.
How to use this result internally
Use the result as a disciplined way to begin a readiness conversation, not as a final audit conclusion.

Trusted IT and cybersecurity partner for New England organizations since 2005.