
Get 24/7 Security Operations Without Building a Security Team.
Vantage MDR puts Vancord analysts behind the tools your IT team already uses—monitoring, investigating and responding within the authority you set.
You keep control. Vancord keeps the security watch.

Higher-Education Organizations Working With Vancord
 Curry College
 Central Connecticut State University
 Connecticut College
 Wesleyan University
 Saint Thomas More at Yale
 Eastern Connecticut State University
 Albertus Magnus College
 Keuka College
Reliable Security Needs Both Expertise and Response Capacity
Automated reporting is not incident response. Someone qualified still has to investigate the signal, decide what is real and act while the evidence is fresh. A capable IT team can have strong tools and still lack continuous specialist capacity when an incident crosses the boundary of routine IT work.
Keuka CollegeFrom ticket submission to live incident-response guidance during a late-night incident.
Keuka's IT team needed help choosing the right next steps. Vancord entered briefed and guided the response.
Read Katey Cheplick's account ↗Where Does Your Current Coverage Still Depend on Internal Availability?
Vantage MDR adds the investigation, escalation and response capacity that security tools alone do not provide. The 12-question assessment helps you identify where that workload still falls back on your IT team—and whether Vantage MDR fits the gap.
Let Your Team Unplug. Vancord Keeps Watch—and Can Respond.
Vancord's 24/7 SOC keeps monitoring and investigating after hours, and can take agreed response actions within the authority you set.
If your team is needed, they come in with the incident already investigated, the current state clear and the next decision defined.
Take the 24/7 Security Workload Off Your Team. Keep Control of Your Environment.
Vantage MDR takes on the continuous monitoring, investigation and agreed response work that would otherwise fall back on your IT team. You keep the institutional context, priorities and authority.
Set context & authority
You define the environment, priorities, escalation paths and what Vancord is authorized to do.
Monitor continuously
Vancord watches the agreed security signals while your IT function keeps running the institution.
Investigate & respond
Analysts validate, filter and act within the response authority already agreed with you.
Decide when needed
You enter only when campus knowledge, authority or direct action is genuinely required.
Document the outcome
Vancord records what happened, what was handled and what reached your team.
Tools Cover Parts of the Lifecycle. Responsibility Has to Cover the Event.
NIST CSF 2.0 organizes cybersecurity around Govern, Identify, Protect, Detect, Respond and Recover. Select a function to see where responsibility can break down—and what Vancord adds.
Govern
Decide how cybersecurity risk is managed: authority, responsibilities, rules and oversight.
Official NIST definition ↗Security may sit inside general IT while after-hours authority and escalation remain less explicit.
Higher-ed evidence ↗You define authority and escalation before an incident; Vancord follows the operating rules you set.
Vancord evidence ↗Identify
Understand the assets, systems, users, suppliers and risks that make up your cybersecurity exposure.
Official NIST definition ↗You know the environment, but maintaining a continuous security picture competes with broader IT ownership.
Higher-ed evidence ↗Vancord reporting shows protected assets, investigated activity and where attention is needed.
Vancord evidence ↗Protect
Use safeguards that reduce the likelihood or impact of cybersecurity events.
Official NIST definition ↗You may already have strong controls. The gap is who watches exceptions and acts when specialist attention is required.
Higher-ed evidence ↗Eligible controls stay in place while Vancord adds human oversight and approved response workflows.
Vancord evidence ↗Detect
Find and analyze possible attacks and compromises quickly enough to understand what is happening.
Official NIST definition ↗Your tools can detect activity around the clock; continuous investigation may still depend on who is available.
Higher-ed evidence ↗Vancord analysts investigate, filter benign activity and escalate validated risk.
Vancord evidence ↗Respond
Take action on a detected incident: analyze it, contain it, communicate and manage the response.
Official NIST definition ↗A real incident can require containment and sequencing beyond the team’s practiced security depth.
Higher-ed evidence ↗Vancord follows agreed response and escalation rules and brings you in with context when your action is needed.
Vancord evidence ↗Recover
Restore affected assets and operations, communicate what happened and improve readiness after the incident.
Official NIST definition ↗Recovery is harder when the incident history is scattered across alerts, tickets and memory.
Higher-ed evidence ↗You enter recovery with a documented investigation, response and notification record.
Vancord evidence ↗Higher-Education Security Experience, Backed by a 24/7 SOC
Vancord gives you a dedicated U.S.-based security team that learns your environment instead of dropping you into an anonymous alert queue.
Vancord has served New England organizations since 2005, with active participation in REN-ISAC, NERCOMP leadership and the Connecticut Higher Education Roundtable for Information Security. Jason Pufahl previously served as UConn's CISO and Director of Infrastructure.
People who learn your environment and escalation rules.
Human monitoring, investigation and response around the clock.
REN-ISAC, NERCOMP and Connecticut higher-education security involvement.
Direct CISO and infrastructure experience from the University of Connecticut.
Know Who Stands Behind the Service
When something important happens, you should know who leads the work and how the security function is managed.

What Gets Handled Before It Reaches You
An example month shows the operating model: Vancord processes the security activity first; your team sees the exceptions that need its knowledge, authority or action.
Example activity. Actual volume varies by environment.
Reviewed by Vancord.
Handled without internal IT.
Closed before escalation.
Specialist judgment applied.
Your context or authority required.
One record of what happened.
Estimated IT Hours Returned
Time kept on campus IT instead of alert triage.
Get Response Gameplans Before Need Arises
You and Vancord establish response plans, escalation rules and authority before an incident. That defines what Vancord can do, when your team is brought in and what happens next—so response does not start from zero.
Vancord validates what is actually happening.
Analysts take the response actions you have already authorized.
You enter when a decision or action genuinely needs you.
See What Vancord Actually Handled
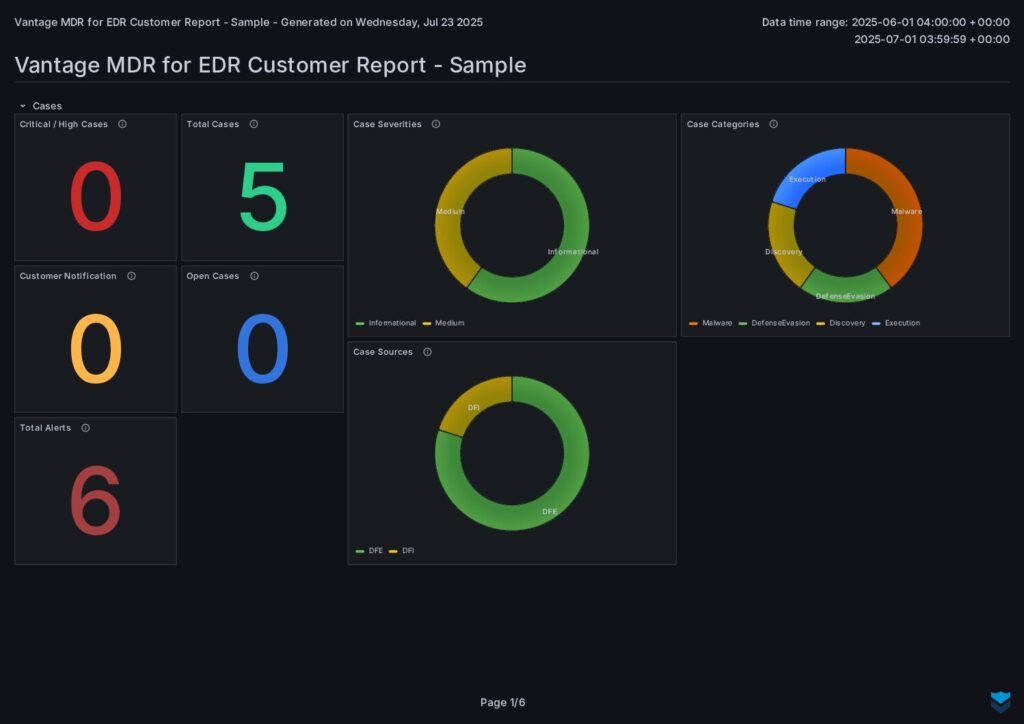
The Vantage MDR report records protected assets, investigated cases, severity, source, resolution and customer notification.
Turn Security Activity Into a Clear Leadership Answer
You get the technical record. The reporting helps you explain coverage, incidents, response and remaining risk without forwarding an alert stream upstairs.
security picture
Coverage
You can show which assets and systems are under coverage, rather than answering with a tool list.
What is protected?What Education IT Leaders Say
Albertus Magnus CollegeThe technicians are ready to help when we have had serious issues with our network
Eastern Connecticut State Universitywe worked with Vancord specifically because in-house staff is difficult to maintain, especially in a higher education sector.
Keuka CollegeWe had a situation and an incident where we didn't really know how to proceed and what the right steps were. I submitted a ticket and had a call within 15 minutes.
Questions You May Have
Will Vancord take control of my network?
No. You retain ownership of the environment. You define what Vancord may do, which actions require authorization and when your team must be involved.
Will every security notification still come to my IT team?
No. Vancord investigates and filters activity before escalation so routine, benign and false-positive events do not automatically become another internal IT task.
What happens when something is real?
Vancord validates the event, follows the agreed response strategy and acts within the authority you set. If you need to become involved, you receive the current state, actions already taken and the next decision.
Do I need to replace the security tools I already have?
Not necessarily. Vantage MDR is designed to add specialist operational capacity behind eligible tools and controls already in place. Vancord confirms compatibility before changes are made.
We already have an MSP. Does Vantage MDR replace them?
It does not have to. The key question is what your MSP already monitors, investigates, contains and reports - and where specialist security responsibility still remains with your team.
Keep Control. Add 24/7 Security Operations Behind Your IT Function.
Vancord monitors, investigates and responds within the boundaries you set - and brings you in when your institution needs you.
Check Your Coverage Gap — 12 Questions ↗