

- cyberliability
Keeping You Proactive
Whether you’re looking to qualify for coverage, reduce your insurance premiums, or be proactive in the face of growing cybersecurity incidents, we offer a range of solutions to keep you covered.
As a trusted partner, Vancord works to assess, implement, and monitor the security of your organization which allows you to qualify for coverage or stay compliant with your insurance provider.
Where does good security come from? It’s not from complicated niche products. Compliant networks and strong cybersecurity are born from sound operational practices and knowledge of infrastructure vulnerabilities and their solutions.
We offer Vulnerability Assessments designed to pinpoint weaknesses in your cybersecurity infrastructure and identify compliance gaps.

Multi-factor Authentication

Backups

Disaster Recovery Planning

Managed Detection & Response
A robust security program does not happen overnight and there is no one size fits all approach when it comes to satisfying your cyber liability insurance carrier. Listen to episode 27 of CyberSoundTM to stay up to date on the latest regarding cyber liability insurance requirements and how we can help.
The Manufacturer’s Guide to CMMC, NIST 800-171, NIST CSF 2.0, ISO 27001
Manufacturers often face overlapping cybersecurity requirements from customers, contracts, and industry standards. The challenge is understanding which requirements are mandatory, and how they work together to build a compliant security...
CTEM vs Vulnerability Management: What’s the Difference?
Your scanner produces a list every month, and your team patches what it can before the next list arrives. Then a vendor says that approach is outdated and that you...
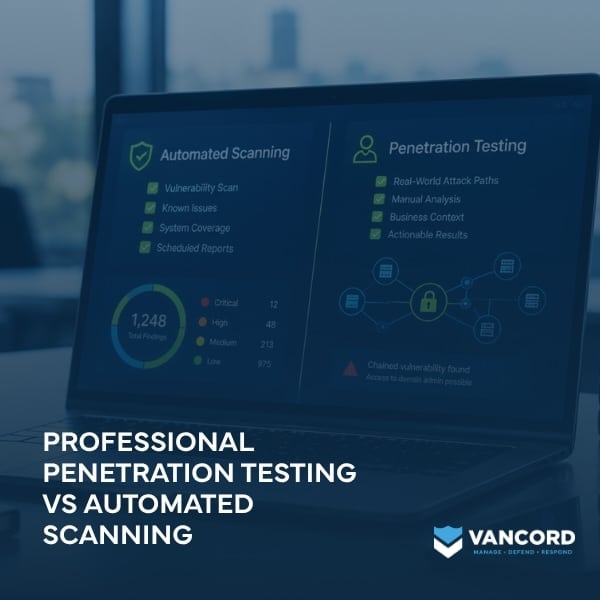
Professional Penetration Testing vs Automated Scanning
A vulnerability scanner can check thousands of systems in a morning and repeat the job every month. What it can’t do is recognize that a medium-severity finding, an overshared file...